WordPress, eCommerce, custom development and high-converting landing pages.
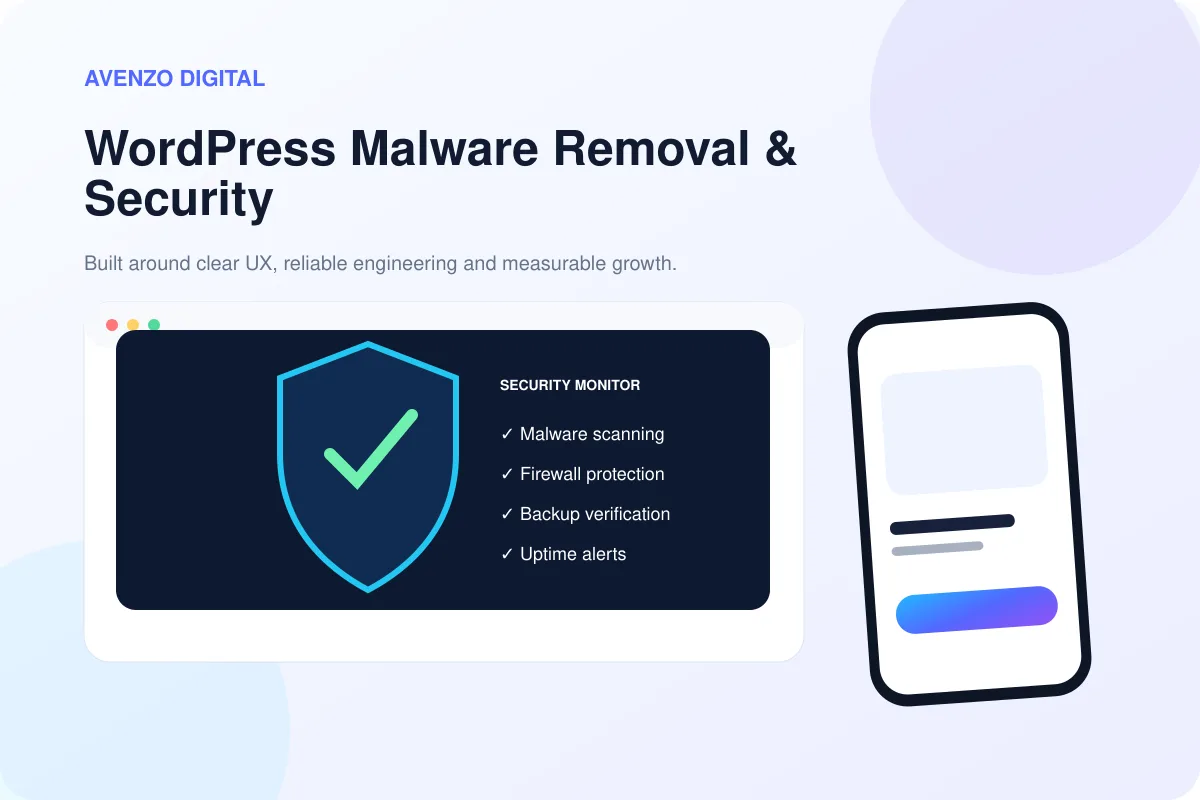
We clean hacked WordPress sites, remove malware completely, and lock down the vulnerabilities that let it in – so your site, your rankings, and your visitors are actually safe, not just patched over.
Not a security plugin installed after the fact. Every cleanup starts with finding exactly how your site was compromised, then removing it completely and closing the door it came through.
Every file, database table, and script checked for injected code, backdoors, and hidden admin accounts, then removed completely - not just the obvious symptoms.
The specific entry point - an outdated plugin, weak password, or exposed file - identified and confirmed, so you know exactly how it happened.
Google Safe Browsing, hosting provider flags, and search engine warnings addressed and cleared once your site is verified clean.
Firewall rules, login protection, file permissions, and admin access locked down so the same vulnerability can't be used again.
A verified clean backup taken once your site is confirmed malware-free, so you always have a safe restore point going forward.
Your site watched for reinfection attempts after cleanup, so a hacker trying the same trick again gets caught immediately.
Running a free scanner and deleting flagged files is fast and often leaves the actual backdoor in place. Here’s what changes when your site is cleaned and secured properly.
FIXES THE ACTUAL CAUSE
Investigation before any files are touched
We identify exactly how the site was compromised and where every piece of injected code is hiding – including backdoors designed to survive a surface-level cleanup – before removing anything.
BUILT TO PERFORM
Every file and database change is checked against a clean baseline, and the site is re-scanned after cleanup to confirm nothing was missed.
MADE TO LAST
Hardening that stops it from happening again
We close the specific vulnerability that let the malware in, not just remove the malware itself, and set up monitoring so reinfection gets caught immediately.
Five phases keep your cleanup organized, transparent, and focused on getting your site clean and staying that way.
We scan your full site and database to identify every instance of malware and the specific vulnerability that let it in.
Malware removed, backdoors closed, and security hardening applied – firewall, login protection, and file permissions locked down.
Post-cleanup monitoring and ongoing security maintenance so reinfection attempts get caught before they succeed.
A cleanup and hardening plan mapped to what was found, reviewed with you before any files are touched.
Full re-scan to confirm the site is clean, plus blacklist and warning removal so your site is trusted again.
We choose the approach based on how your site was compromised and how it’s hosted – not a bundled plugin stack applied to every site the same way.
Every cleanup is scoped individually – these tiers give you a starting point for the conversation.
For a site that’s currently hacked, blacklisted, or showing malware warnings.
For businesses that want the cleanup plus ongoing protection.
For high-traffic, e-commerce, or multi-site environments with critical uptime needs.
Share your current website, what you’re seeing (warnings, blacklisting, strange behavior), and how urgent it is. Our team will review your site and recommend a suitable approach.
No pressure and no generic package. We will review your requirements before recommending a solution.